Network & Security Infrastructure — IF5000
Hardened multi-service Linux server built with a team of 4: Docker workloads, a Tailscale VPN, Suricata IDS and a real-time security alerting pipeline.
Role: Team of 4 — shared hands-on configuration and hardening of the server (work happened directly on a shared virtual machine, not through individual git commits)
Team
Team of 4
Timeline
Jun 2026
Type
Academic
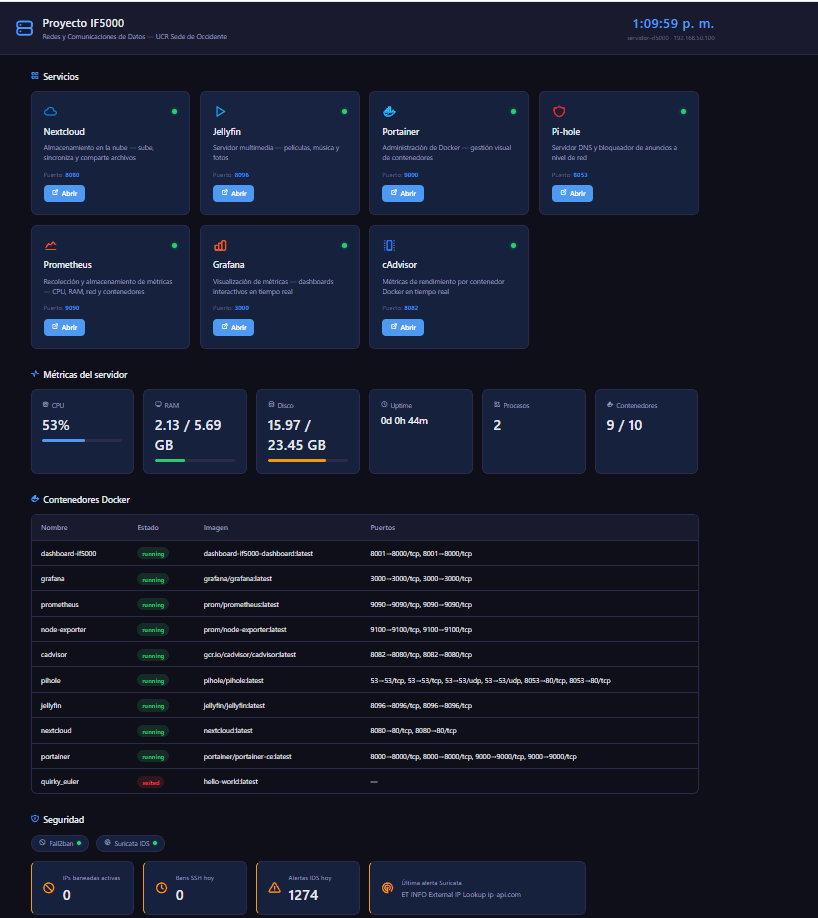
Dashboard
01 · Context & Problem
What problem this solves
The IF5000 Networks course required standing up an Ubuntu Server VM exposing Docker services (storage, media, DNS, remote admin), reachable over SSH and a VPN, with optional bonus tracks for monitoring and performance. My team of 4 built and hardened the full stack together on one shared VM.
02 · Solution
What it actually does
One hardened Ubuntu Server 24.04 VM running Docker workloads, a Tailscale mesh VPN for stable remote access, and a layered security setup: Suricata IDS, Fail2ban, and a custom Bash-based alerting pipeline posting to Discord.
- Docker services: Nextcloud, Jellyfin, Pi-hole and Portainer, each on its own mapped port to avoid collisions.
- Tailscale VPN giving the team a stable address to reach every service from any network, used for all remote demos.
- A Prometheus + Grafana + Node Exporter + cAdvisor monitoring stack (the course's optional monitoring bonus track).
- Suricata IDS running the Emerging Threats Open ruleset, logging structured alerts.
- Fail2ban banning repeated failed SSH attempts.
- A custom SOC pipeline: independent Bash watchers tail Suricata's alert log, Fail2ban's ban log and the SSH auth log, aggregate and correlate events, enrich attacker and login IPs with geolocation, and post formatted alerts to a Discord channel in real time.
03 · Architecture
Architecture & decisions
A single Ubuntu VM with a static IP via Netplan, a flat Docker bridge network, and Tailscale as the primary remote-access path used in demos, alongside direct LAN access.
Three of the alerting watchers run as always-on systemd services.
Turns ad hoc detection scripts into durable daemons that restart automatically and log through journalctl.
The Suricata watcher aggregates alerts in a 60-second window per IP and signature before notifying.
Avoids flooding the team's Discord channel with a message per packet during a real scan.
04 · Stack
Full stack, by layer
Infrastructure & Deploy
Auth
External Services
05 · Challenges
Technical challenges solved
Avoiding alert fatigue on a real IDS feed
Problem: A naive per-alert notification would flood the team's channel during an active scan.
Solution: Built a dedup/aggregation window keyed by source IP and signature, flushing one summary message every 60 seconds instead of one message per matched packet.
Correlating signals across three independent log sources
Problem: Suricata alerts, Fail2ban bans and SSH auth events each lived in a different log with no shared identifier.
Solution: Wrote a scoring correlation script that raises a source IP's threat score when it appears across multiple sources (a scan signature, a Fail2ban ban, an HTTP probe pattern), firing a distinct "correlated threat" alert once a threshold is crossed.
Telling a new login from a known one
Problem: Plain login logging doesn't distinguish a user's usual device from a new, potentially suspicious one.
Solution: The SSH watcher tracks each user's last-seen IP in memory and geolocates it, flagging logins from an IP it hasn't seen before for that user.
06 · Results
Results
Delivered a working multi-service hardened server with real-time security alerting, demoed end to end for the course.
No hard metrics confirmed yet for this project — the impact above is qualitative only.
07 · Retrospective
What I'd do differently
Coordinating a real-time alerting pipeline across three independent log sources, with each teammate owning a different watcher script, was a good lesson in keeping a shared contract (the Discord message format, the log paths) consistent across code nobody centrally reviewed.
Have a system that needs building?
Tell me what you're running today and what's breaking. I'll tell you honestly whether I can help.